

Adding RADIUS Server(s)
Applies to version(s): v2.7
Multiple RADIUS servers can be configured to provide RADIUS redundancy.
1- Select RADIUS from the navigation panel.
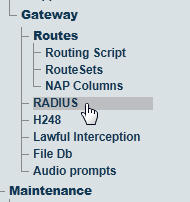
2- In the Editing RADIUS client configuration page, select Create new RADIUS server

3- Configure the RADIUS server with these parameters:
Name to recognize the server.
Server IP address is the IP address of the RADIUS server.
Server UDP port is the UDP port of the RADIUS server.
Public IP address The IP address that will be set in the NAS-IP-Address attribute, when present. This is used when the RADIUS client is behind a NAT. Leave this field empty in order to use the source IP address instead.
Timeout The time to wait (in milliseconds or seconds) for a response from the RADIUS server before retrying.
Retries is the number of times to send the same request again when the timeout is reached. See full details on functionality here: CDR redundancy
Server type is the type of RADIUS server this configuration corresponds to. The choices are Accounting for CDR functionality and Authorization for authentication and authorization.
Associated server is used to link Accounting and Authorization servers together. See full details on functionality here:ACCT/AUTH Association
Use polling (Status-Server) dictates if polling with the Status-Server message is supported by this server. When enabled, this option allows the RADIUS client to recognize quickly and efficiently if the RADIUS server is available or not.
Polling Delay The time to wait (in milliseconds or seconds) before polling the server.
Server secret is the passphrase to authenticate the TMG on the RADIUS server.
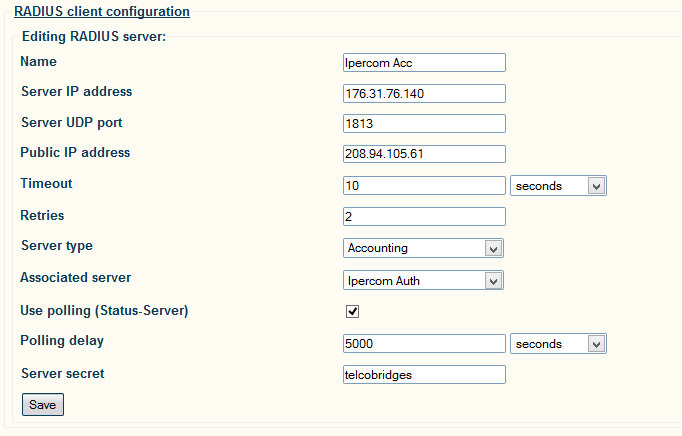
4- You can configure multiple RADIUS servers to have RADIUS redundancy. Each entry can have different settings.

Last updated
Was this helpful?